Explore professors working in differential privacy and related research areas.
Use YourScholar to discover research opportunities and identify
professors whose work aligns with your academic interests.
Professors in Differential Privacy
Showing page 1 of 1 —
14 professors available publicly
Vitaly Shmatikov
Privacy Enhancing Technologies (PET)
Security and Privacy in Machine Learning
Adversarial Machine Learning
Vitaly Shmatikov is a professor of computer science at Cornell Tech and the Cornell Ann S. Bowers College of Computing and Information Science. Before Cornell, he worked at the University of Texas at Austin and SRI International. His research areas include digital privacy, comput...
Adam Smith
Data Privacy
Cryptographic Protocols
Differential Privacy
Adam Smith is a Professor of Computer Science and Engineering at Boston University. His research interests lie in data privacy and cryptography, and their connections to machine learning, statistics, information theory, and quantum computing. He obtained his Ph.D. from MIT in 200...
Kobbi Nissim
cryptography
differential privacy
privacy law and policy
I am a Professor at the Department of Computer Science, Georgetown University and an Affiliate Professor at Georgetown Law. Prior to joining Georgetown, I was at the Department of Computer Science, Ben-Gurion University. From 2012 to 2017 I visited the Center for Research in Comp...
Daniel Kifer
Differential Privacy
Pufferfish Privacy Framework
L-diversity
Daniel Kifer is a Professor in the Department of Computer Science and Engineering at Pennsylvania State University, where he serves as the Director of the Center for Machine Learning and Applications (CMLA). His research is focused on the intersection of Statistical Privacy, Mach...
Sewoong Oh
differential privacy
secure machine learning
robust machine learning
Sewoong Oh is a Professor at the Paul G. Allen School of Computer Science & Engineering at the University of Washington. Previous to joining University of Washington in 2019, he was at the department of Industrial and Enterprise Systems Engineering at University of Illinois at Ur...
Jonathan Ullman
Differential Privacy
Statistical Validity in Privacy
Robustness in Machine Learning
Jonathan Ullman is an associate professor in the Khoury College of Computer Sciences at Northeastern University, based in Boston.
Ullman's research centers on the foundations of privacy for machine learning and statistics, namely differential privacy and its surprising interpl...
Tianhao Wang
differential privacy
machine learning privacy
privacy-preserving algorithms
About me
I am an assistant professor at the University of Virginia. I got my PhD from Purdue University and my Bachelor’s degree from Fudan University. I work on differential privacy and machine learning privacy, focusing on designing algorithms that work in practice.
Erman Ayday
Genomic Data Privacy
Differential Privacy
Secure Data Analytics
Erman Ayday, Ph.D., is an Associate Professor in the Department of Computer and Data Sciences at the Case School of Engineering, Case Western Reserve University. He earned his Ph.D. (2011) and M.S. (2007) in Electrical and Computer Engineering from the Georgia Institute of Techno...
Yuan Hong
differential privacy
secure computation
applied cryptography
Dr. Yuan Hong is a Collins Aerospace Endowed Associate Professor in the School of Computing at University of Connecticut (UConn) and affiliated with the Connecticut Advanced Computing Center (CACC). Prior to joining UConn, he was an Assistant Professor in Computer Science and Cyb...
Depeng Xu
differential privacy
algorithmic fairness
ethical AI
Dr. Depeng Xu is an Assistant Professor in the Department of Software & Information Systems and the School of Data Science at UNC Charlotte. His research focuses on data mining and machine learning, specifically differential privacy, algorithmic fairness, and ethical AI
Lydia Zakynthinou
Differential Privacy
Privacy-Preserving Machine Learning
Robustness in Learning Algorithms
Lydia Zakynthinou is an assistant professor in the Department of Computer Science and a member of the Johns Hopkins Data Science and AI Institute. She works on the theoretical foundations of trustworthy and reliable machine learning and statistics.
Her research focuses on deve...
Gavin Brown
Differential Privacy
Machine Learning Model Memorization
Privacy-Preserving Statistical Algorithms
I am an assistant professor at the University of Wisconsin–Madison in the Department of Computer Sciences. Prior to that, I was a postdoc at the University of Washington with Sewoong Oh. I completed my PhD at Boston University, where I was advised by Adam Smith.
I work on ma...
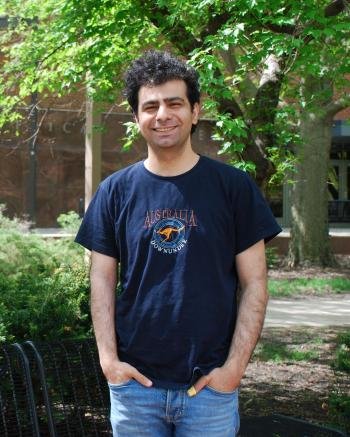
Meisam Mohammady
Differential Privacy
Adversarial Robustness in Machine Learning
Fairness in Machine Learning
Dr. Meisam Mohammady is an Assistant Professor in the Department of Computer Science at Iowa State University (ISU), where his research focuses on developing responsible Machine Learning methods that are privacy-preserving, adversarially robust, and fair, leveraging tools such as...
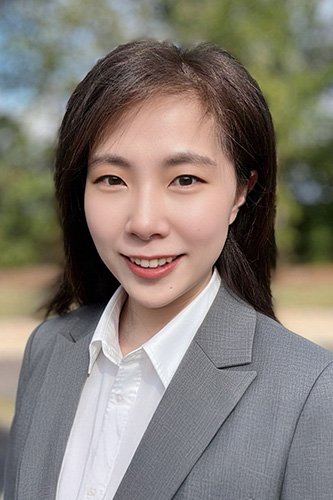
Emily (Shuya) Feng
Privacy-Preserving Machine Learning
Differential Privacy
Large Language Model Security
Emily (Shuya) Feng is an Assistant Professor in the Department of Computer Science at the University of Alabama at Birmingham, starting in August 2025.
Dr. Feng's research addresses fundamental challenges in AI security and privacy, encompassing privacy-preserving machine lea...